01
Intake
Finalize bytes/profile/custody; receipt differs from evidence readiness.
Archive Service
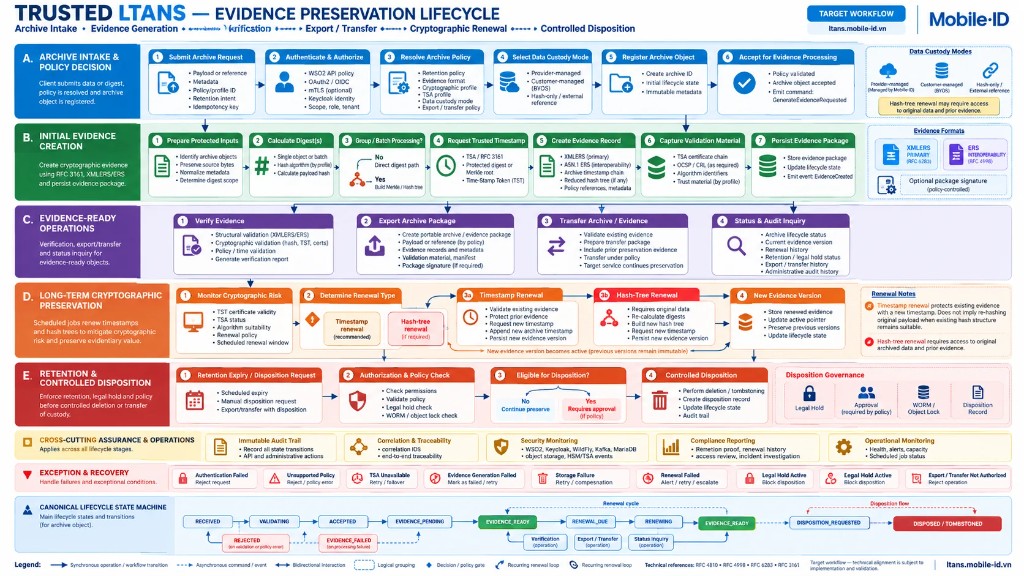
Seven control points from source freeze to disposition, with distinct guards, owners, artifacts and exceptions.
Each point has distinct authority, guards and artifacts. Verification, holds and permission changes can recur; this is not a one-pass linear pipeline.
| View | Content |
|---|---|
| Owner | Record owner |
| Guard | Bytes/revision, members, custody and rights |
| Artifact | Source inventory; no LTANS evidence yet |
| Exception | Missing data/rights: resolve before submission |
| View | Content |
|---|---|
| Owner | Archive Service |
| Guard | Authentication, profile, digest and idempotency |
| Artifact | archiveId/jobId receipt; not EVIDENCE_READY |
| Exception | HTTP disconnect: reconcile original transaction |
| View | Content |
|---|---|
| Owner | Evidence + Trust |
| Guard | Pinned input and approved TSA |
| Artifact | Stored/validated revision or explicit failure |
| Exception | TSA/storage failure never becomes success |
| View | Content |
|---|---|
| Owner | Renewal + Policy |
| Guard | Monitor risk, retention and reread rights |
| Artifact | Schedule/decision and continuation revision |
| Exception | HASH_TREE without bytes blocks |
| View | Content |
|---|---|
| Owner | Record owner / verifier |
| Guard | Access rights and evaluation context |
| Artifact | Step report and scoped export |
| Exception | SUCCEEDED does not imply VALID |
| View | Content |
|---|---|
| Owner | Sender + recipient |
| Guard | Package, manifest, tools and acknowledgement |
| Artifact | Recorded responsibility-transfer point |
| Exception | Export completion is not recipient acceptance |
| View | Content |
|---|---|
| Owner | Data owner + approver |
| Guard | Retention, every hold, storage locks and backups |
| Artifact | Per-target outcome and retained residuals |
| Exception | Expiry never auto-deletes; partial failures retain checkpoints |

Block disposition of case-scoped records until an authorized hold-release decision.
View service mechanics →
Three custody models, reread access and lifecycle data/key responsibilities.
View details →
Versioned policy configuration, effective conditions and record-level history.
View details →
Observe jobs, storage/TSA dependencies, incidents and post-recovery consistency.
View details →| Time | Interpretation |
|---|---|
| Business date | Source-declared issue/transaction date; retain provenance and authority. |
| Receipt time | Service records receipt; evidence generation may still be pending. |
| genTime | Time in a verified TSA token; check digest binding and source. |
| evaluatedAt | Report evaluation time; read with policy, evidenceVersion and trust context. |
An old source date does not create historical evidence. Retain the source date/provenance; receipt or a new token cannot establish historical attestation.
01Finalize bytes/profile/custody; receipt differs from evidence readiness.
Archive Service 02
Check digest/token/syntax, persist revision, then emit EvidenceGenerated.
Evidence Service 03
Select revision/context; read steps/outcome rather than Job alone.
Verification Service 04
Assess risk/select mode and retain predecessor/successor history.
Renewal & Crypto-Agility 05
Recipient checks package/scope; acknowledgement does not delete source.
Export & Transfer 06
Check retention, all holds, authority and each target before effects.
Controlled DispositionPrior evidence and suitable hash conditions; extend timestamp protection under the profile.
Needs originals, prior evidence and read/decrypt access; new digest/tree and timestamp.
The modes are conditional alternatives, not a mandatory sequence. Missing prerequisites stop/reconcile work; do not switch modes to hide failure.