MOBILE-ID · TRUSTED LTANS
Independent Verification
Reproduce evidence evaluation from exported material, originals and independently selected trust inputs.
Verification outside the operating environment
The recipient selects suitable tools and trust sources rather than only reading the provider API conclusion. Obtain exact bytes, evidence, history and assessment material. Content access is separately authorized.
| Step | Action and retained result |
|---|---|
| Receive and freeze | Retain package, manifest, exportId, scope and trusted-channel digest. |
| Inventory and bytes | Check all files, sizes, paths and digests; missing files prevent inventory completeness. |
| Decode structure | Use a syntax/profile-appropriate ERS/XMLERS decoder; separate parse and certificate errors. |
| Data binding | Recompute digests/tree paths binding exact bytes to archive timestamps. |
| Tokens and trust | Check signature, imprint, policy, path and status at the relevant time. |
| Renewal history | Check predecessor/successor bindings and algorithms under the profile. |
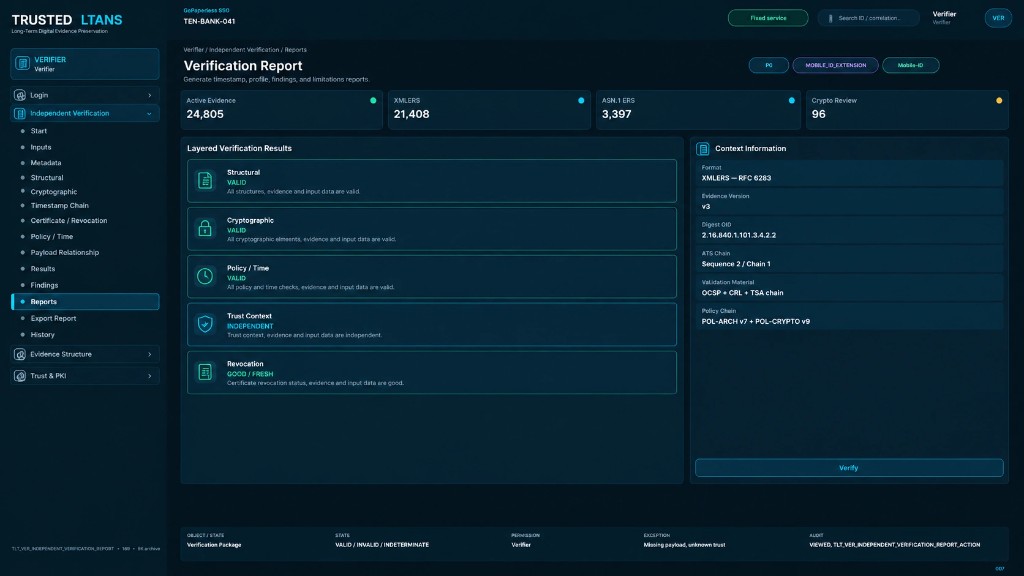
| Report | Record tool/version, time, policy, trust anchors, individual checks and limitations. |
| Scope acknowledgement | Acknowledge the exact package/scope after reconciliation; no automatic source deletion. |
What the bundled sample establishes
The bundled synthetic dossier runs inventory/hashing with standard Python; it contains no verified TSA token or ERS/XMLERS. Steps 3–6 therefore cannot be claimed as cryptographic verification. Use the procedure as a checklist when a real package is provisioned.
python3 samples/verify_sample.py samples/reference-dossier