Register source
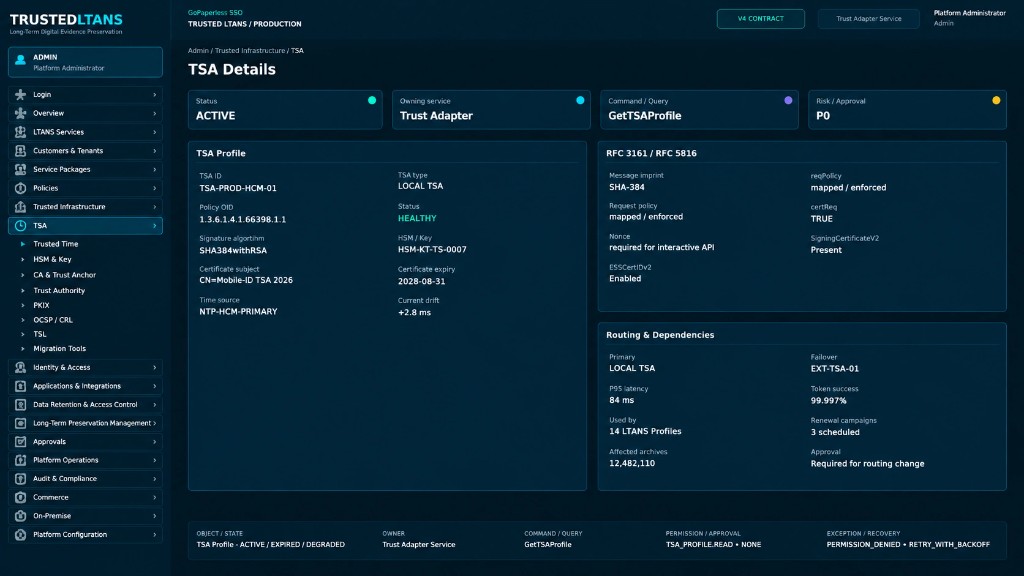
Source profiles identify CA/TSA, certificates, trust anchors, policy OIDs and applicable CP/CPS/TSA documents.

Timestamping, certificate paths, status data and key configuration for verification.
Supply versioned trust inputs for evidence generation and validation while retaining historical context.
| Prepare | Receive |
|---|---|
| Timestamp request, trust anchors, TSA certificates, OCSP/CRL, evaluation time and HSM/KMS configuration. | Validated token, versioned trust path and certificate-status result with freshness bounds. |
Participants: Trust-source administrators, key custodians and relevant TSA/CA operators.
Source profiles identify CA/TSA, certificates, trust anchors, policy OIDs and applicable CP/CPS/TSA documents.
Check signatures, digest binding, time and status material. Timeout and UNKNOWN require distinct outcomes.
Retain references or hashed copies under policy and record collection/evaluation times; current data does not replace historical inputs.
Fallback TSAs require approved conditions; new source revisions need compatibility tests and retained history.
| Current | Guard | Actor | Next | Artifact / recovery |
|---|---|---|---|---|
| Proposed source [model] | Check CA/TSA, policy and interface | Trust administrator | Approved source [model] | Keep tests and version; a provider logo is not interoperability proof. |
| Response received [model] | Validate signature, imprint, time and status | Trust Adapter | Accept / reject / insufficient [model] | UNKNOWN differs from GOOD; timeout is not revocation. |
| Source rotation [model] | Fallback meets approved controls | Trust + Operations | New source revision [model] | Retain historical material/origins; do not overwrite old certificates. |
| Situation | Action | Boundary |
|---|---|---|
| OCSP UNKNOWN | Record unknown status and apply policy. | Do not infer GOOD. |
| Key or certificate changes | Rotate and check bindings under the profile. | Do not overwrite historical source profiles. |
| HSM/KMS not provisioned | Identify a deployment dependency. | No claim of protection by an unprovisioned HSM. |
Check TSA EKU, MessageImprint, ESSCertIDv2 when applicable and OCSP freshness. HSM protects keys; it does not by itself establish evidence validity.
OCSP UNKNOWN differs from GOOD. Apply an explicit failure policy; obtain suitable CRL/OCSP material or mark evaluation INDETERMINATE.
Retain TSA certificates, trust inputs, token digest, OCSP/CRL results and evaluation time; do not replace historical inputs with current status.
MessageImprint, untrusted certificates and OCSP UNKNOWN must produce distinct reasons.This module includes administration without a public write endpoint. Review interface scope and deployment conditions.
| Element | Definition |
|---|---|
| Input | Timestamp request, trust anchors, TSA certificates, OCSP/CRL, evaluation time and HSM/KMS configuration. |
| Output | Validated token, versioned trust path and certificate-status result with freshness bounds. |